





Introducing Observeri’s Continuous Attack Surface Management: See Your Blind Spots Before Attackers Do
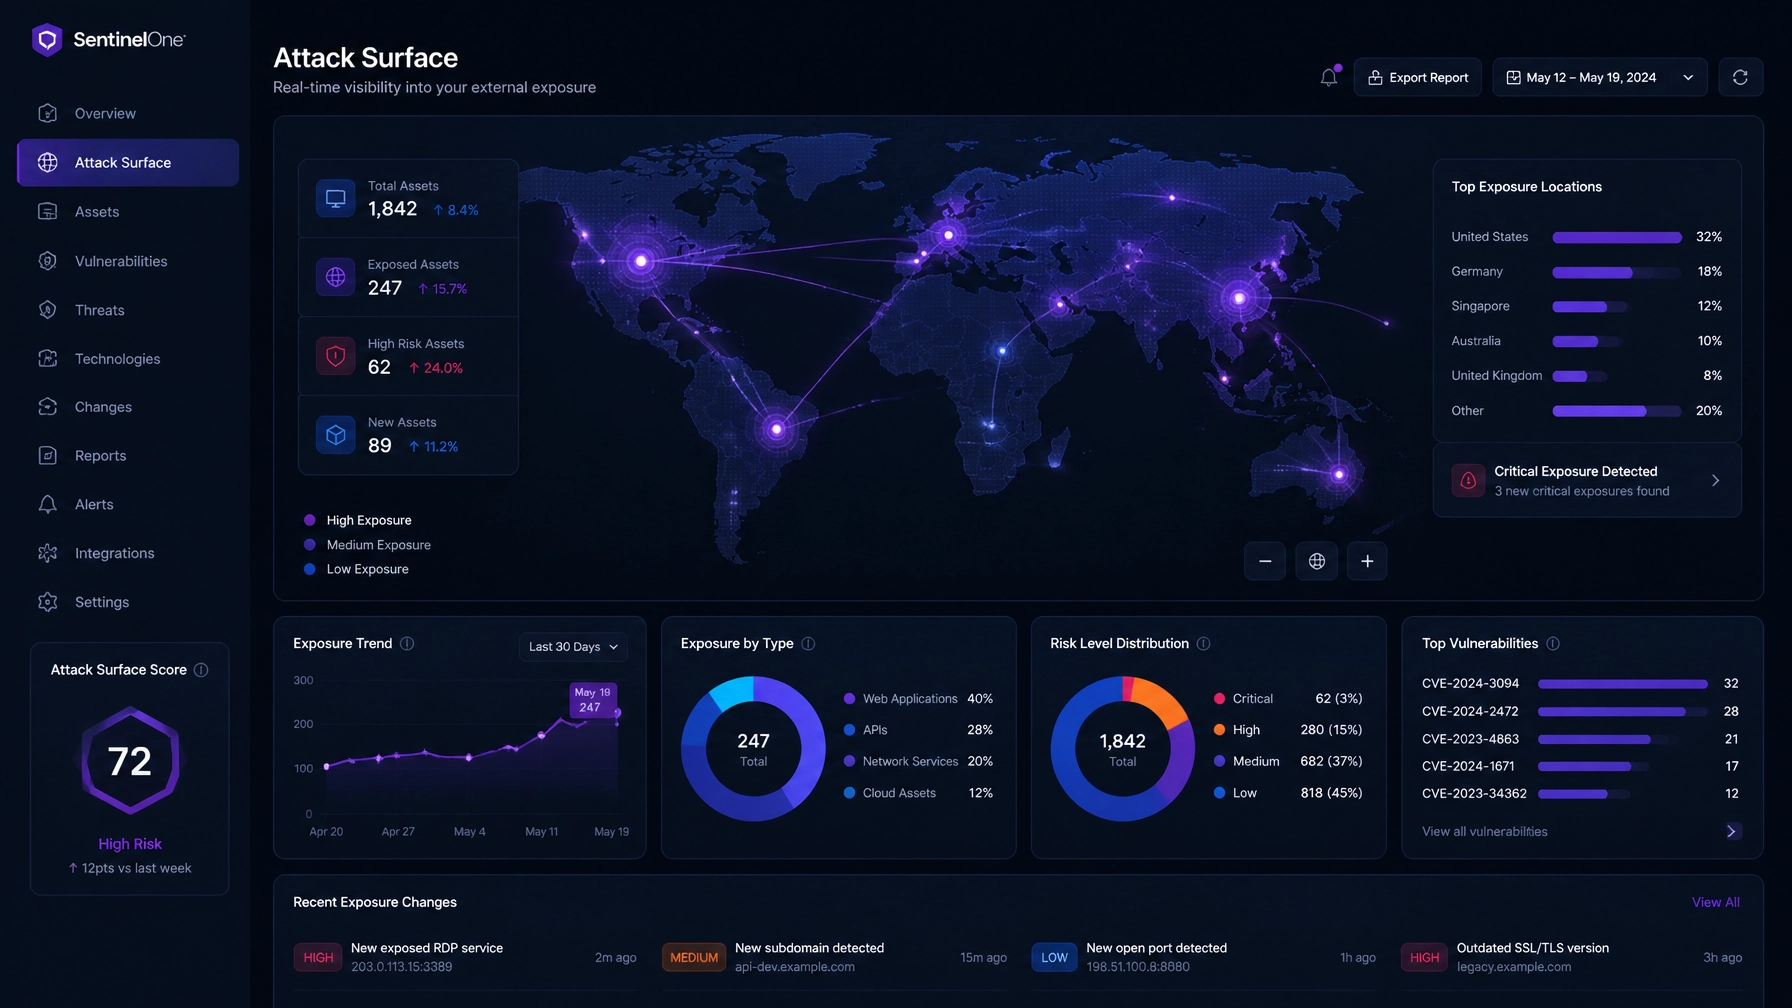
Security teams are currently losing a battle of visibility. While most organizations focus on hardening their known assets, the modern enterprise perimeter is no longer a fixed line: it is an amorphous, shifting landscape of cloud instances, forgotten subdomains, and shadow IT.
The data is clear: 70% of organizations have experienced a breach originating from unknown or unmanaged internet-facing assets.
At Observeri, we believe you cannot secure what you cannot see. Today, we are proud to announce the launch of our Continuous Attack Surface Management (CASM) module. This isn't just another standalone discovery tool. It is a fully integrated engine that feeds real-time telemetry directly into the Observeri GRC platform, transforming technical vulnerabilities into quantified business risks.
The Visibility Gap: Why Legacy Security is Failing
The Attack Surface Management (ASM) market is projected to grow from $1.54B in 2025 to $2.03B by 2026, a staggering 31% CAGR. This rapid growth is driven by one simple reality: legacy, point-in-time penetration tests and monthly vulnerability scans are obsolete before the report is even finished.
The average organization discovers over 13,000 exposures annually, yet most only manage to remediate 50%. The result? A widening "remediation gap" that attackers exploit within hours of a new vulnerability going public.
Observeri’s CASM module closes this gap by moving from reactive scanning to proactive, continuous defense.
1. Unified Cloud & Public Asset Discovery
Modern enterprises operate across multi-cloud environments (AWS, Azure, GCP), often without a centralized inventory. Our CASM module performs continuous, non-intrusive scanning of your entire public-facing footprint.

- Asset Discovery: Automatically identify subdomains, IPs, and certificates associated with your organization.
- Shadow IT Mapping: Detect unsanctioned cloud environments or "orphan" assets created by DevOps teams that lack official security oversight.
- Cloud Integrity: Verify that your cloud buckets and storage instances aren't accidentally exposed to the public internet.
2. Intelligence-Driven Vulnerability Prioritization
Technical teams are drowning in CVSS scores. A "Critical" vulnerability on a staging server is not the same as a "Critical" vulnerability on your primary payment gateway.
Observeri contextualizes vulnerability assessments using Real-Time Threat Intelligence. We don't just tell you what is broken; we tell you what is being actively exploited in the wild. By focusing on exploitability and business context, we help your team prioritize the 5% of vulnerabilities that pose 95% of your actual risk.
3. Dark Web Monitoring: Outside-In Intelligence
Security doesn't end at your firewall. Attackers often trade stolen credentials, leaked databases, and organizational blueprints on the dark web long before an active breach is detected.

Observeri’s CASM module monitors underground forums, paste sites, and encrypted chat groups for:
- Leaked Credentials: Identify compromised employee accounts before they are used for credential stuffing.
- Stolen Data: Detect if your proprietary data or customer information has been offloaded.
- Brand Sentiment: Track chatter among threat actors specifically targeting your industry or organization.
4. Breach & Attack Simulation (BAS)
Why wait for a real attack to find out if your defenses work? Our module includes automated Breach & Attack Simulation (BAS).

Unlike traditional pen testing, BAS runs continuous, safe simulations of real-world attack vectors. It validates whether your existing controls: EDR, WAF, and Firewalls: actually stop the latest TTPs (Tactics, Techniques, and Procedures). If a simulation succeeds, Observeri creates an immediate risk entry, allowing you to patch the gap before an adversary finds it.
The GRC Advantage: Turning "Noise" into "Numbers"
The primary differentiator of Observeri is our ability to integrate CASM findings directly into our AI-Powered GRC Platform. Standalone ASM tools provide a list of problems; Observeri provides a narrative for the boardroom.
Financial Risk Quantification
Technical vulnerabilities are automatically translated into Expected Annual Loss (EAL).
- CISO: "We have 500 unpatched assets." → CFO: "We have a $2.4M financial exposure due to unmanaged cloud instances."
This shift allows leadership to budget based on dollar impact rather than abstract scores, accelerating decision velocity.
Automated Compliance Mapping
CASM findings are instantly mapped to regulatory frameworks like ISO 27001, NIST CSF, SOC 2, and GDPR. When a new exposed endpoint is discovered, Observeri identifies which compliance controls are now "at risk," automating the evidence collection and remediation workflow.

Operating Reality: The Case for Continuous Resilience
In the Middle East: specifically in high-growth hubs like Dubai and Abu Dhabi: enterprises are prime targets for sophisticated cyber campaigns. Relying on "compliance-as-a-project" is a liability.
Observeri’s CASM module is built for the Operating Reality of 2026. It is designed to provide:
- 12-27X ROI in the first year by consolidating disparate tools.
- 30-90 Day Predictive Breach Analytics through proactive surface monitoring.
- Audit Compression: Reduce the time spent on manual compliance mapping by up to 80%.
Take Control of Your Attack Surface
The perimeter is gone, but your responsibility to protect it remains. Don't let your "blind spots" become an attacker's entry point.
Book a demo with Observeri today to see your organization through the eyes of an attacker and quantify your risk in real-time.